 PluginStats
eslint-plugin-anti-trojan-source weekly downloads statistics
By lirantal · npm · ESLint plugins
ESLint plugin to detect and stop Trojan Source attacks
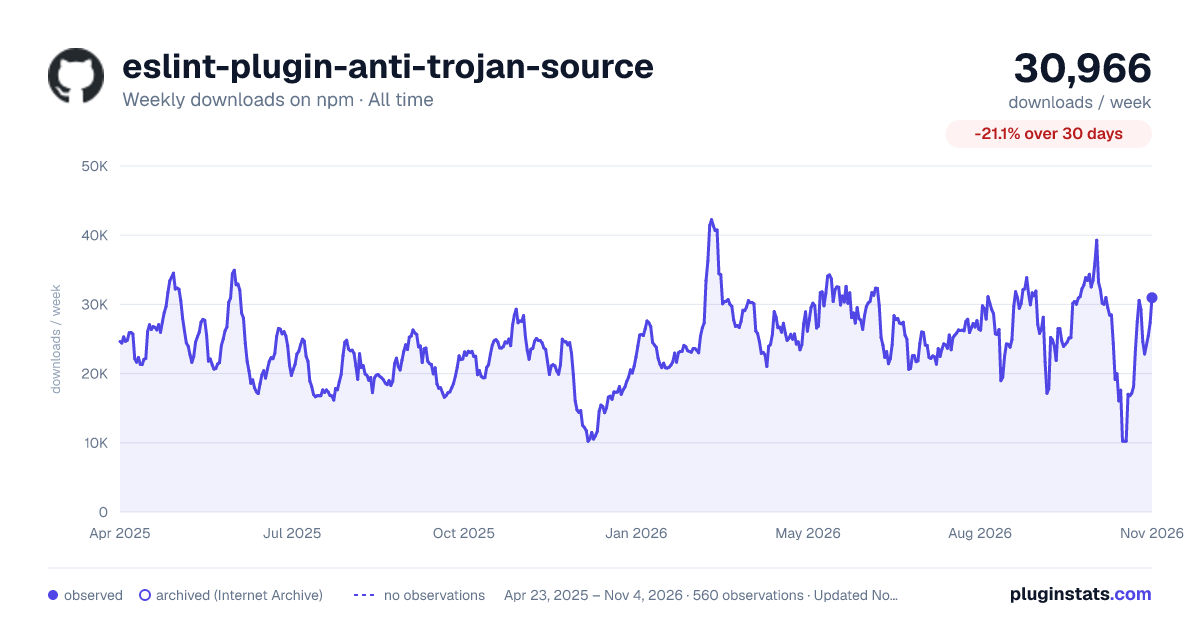
eslint-plugin-anti-trojan-source has 17,592 recorded weekly downloads on npm, a decrease of 27.4% over the past 30 days, ranking #819 of 2,322 tracked listings.
About eslint-plugin-anti-trojan-source
About
ESLint plugin to detect and stop Trojan Source attacks from entering your codebase.
If you're unaware of what Trojan Source attacks are, or how unicode characters injected into a codebase could be used in malicious ways, refer to the README of the anti-trojan-source source code repository.
This ESLint plugin is based on the library and command-line tool anti-trojan-source.
👋 Jan 2023 Update:
This plugin inspired work to create an anti-trojan rule detect-bidi-characters in eslint-plugin-security and if you're already using that security plugin then it is advised to turn on that rule.
Install
npm install --save-dev eslint-plugin-anti-trojan-source
Usage
Once you've installed this plugin, add it to your eslint configuration as follows.
Recommended
This plugin exports a recommended configuration.
To enable this configuration, extend it in the configuration for your project.
{
  "extends": ["eslint:recommended", "plugin:anti-trojan-source/recommended"]
}
Manual
First, you need to define it as a plugin:
Note: ESLint plugins can have their eslint-plugin prefix omitted when they are specified.
{
  "plugins": ["anti-trojan-source"]
}
Then, add an ESLint rule that halts if it finds a Trojan Source attack:
"rules": {
    "anti-trojan-source/no-bidi": "error"
}
Following is a complete example of configuration if you are defining ESLint configuration in your package.json file:
"eslintConfig": {
    "plugins": [
        "anti-trojan-source"
    ],
    "rules": {
        "anti-trojan-source/no-bidi": "error"
    }
}
Example output
The following is an example output when the plugin finds a Trojan Source attack in your codebase:
/Users/lirantal/projects/repos/@gigsboat/cli/index.js
1:1 error Detected potential trojan source attack with unicode bidi introduced in this comment: ' } if (isAdmin) begin admins only ' anti-trojan-source/no-bidi
1:1 error Detected potential trojan source attack with unicode bidi introduced in this comment: ' end admin only { ' anti-trojan-source/no-bidi
/Users/lirantal/projects/repos/@gigsboat/cli/lib/helper.js
2:1 error Detected potential trojan source attack with unicode bidi introduced in this code: '"user // Check if admin "' anti-trojan-source/no-bidi
Documentation
- Project documentation - development, testing, architecture, and conventions.
Contributing
Please consult CONTRIBUTING for guidelines on contributing to this project.
Author
eslint-plugin-anti-trojan-source © Liran Tal, Released under the Apache-2.0 License.
Description from the npm listing.
- eslint
- eslint-plugin
- eslintplugin
- plugin
- eslint plugin
- rules
- trojan
- trojan source
- source
- unicode
- bidi
- bidirectional attacks
- bidi attacks
- bidi security
- unicode security
- attacks
- security
README badge
Show your rank in a README or on your website. The badge updates automatically.
Charts
Images: 30d · 1y · all time · 1600×900 dark



Adoption over time
7/30/90-day growth
Ranking history
Listing placement
Listing placement
Filled points are observed values; hollow points come from Internet Archive snapshots of the listing page. Dashed segments span periods with no observations — values between points are not interpolated.
Each band is one page of 20. Weekly downloads on a linear scale. Placement is projected from weekly downloads, so it can differ from the marketplace's own sort order. Hover a dot to see the listing.
Recent observations
Full history (544)Similar npm ESLint plugins plugins
All 20 eslint-plugin-anti-trojan-source alternatives- 17.6K weekly downloads-41.5%
- 17.4K weekly downloads-52.0%
- 17.1K weekly downloads-35.9%
- 18.2K weekly downloads-41.1%
- 16.8K weekly downloads-56.9%
- 16.7K weekly downloads-51.8%
Data source
Weekly downloads (trailing 7 complete days) come from the official npm downloads API. Downloads include CI and mirrors and are not equivalent to installs or users. npm publishes no ratings.
Listing: https://www.npmjs.com/package/eslint-plugin-anti-trojan-source. First seen Oct 16, 2026; last successful collection Oct 20, 2026. See the methodology.