 PluginStats

Package Checker downloads statistics
By JetBrains s.r.o. (640 listings) · JetBrains Marketplace · Code Editing
This plugin checks your third-party dependencies for known vulnerabilities. It suggests a safe version, if available, to make your code more secure. It also scans...
Package Checker has 21,922,086 recorded downloads on JetBrains Marketplace, ranking #23 of 2,502 tracked listings.
Rating: 4.71 / 5 from 7 ratings
About Package Checker
This plugin checks your third-party dependencies for known vulnerabilities. It suggests a safe version, if available, to make your code more secure. It also scans source code for vulnerable API calls to highlight the most critical problems.
The following package managers and build files are supported:
• Amper build system (module.yaml, module.amper, project.yaml, project.amper, and module template files) • Gradle (build.gradle, build.gradle.kts) • Maven (pom.xml, pom-4.0.0.xml, pom.*, .pom) • npm, pnpm and Yarn (package.json) • PyPI (setup.py, requirements.txt) • Poetry and Pipenv (pyproject.toml, Pipfile) • Go Modules (go.mod) • Composer (composer.json) • JPS - JetBrains Project System (.iml) • sbt (build.sbt), provided by the Scala plugin
The plugin provides the following security inspections:
• Vulnerable declared dependency scans packages defined in your code (such as packages added to a supported build file).
• Vulnerable imported dependency detects packages that are not defined in the source code (such as transitive dependencies).
• Vulnerable API usage shows vulnerable methods and functions in Java source code (out of the box) and in Kotlin source code (if you have the Kotlin plugin installed).
• Malicious dependencies detects malicious NPM and PyPI dependencies in your project to prevent your software from being compromised.
Vulnerable API inspections are language-specific and provided as part of the corresponding language plugins: JavaScript and TypeScript, Python, and Go.
Here is a list of the plugins required to support the related functionality: Gradle, Maven, JavaScript and TypeScript, Python, Go, PHP, and Scala.
Problems identified by Package Checker are reported on the Problems | Vulnerable Dependencies tab. The plugin also provides the Analyze | Vulnerable Dependencies action.
Package Checker doesn't send information about packages to the JetBrains server in cleartext form. It sends only hashed names of packages. We never log or process hashes we don't have in our database, and we don't analyze your proprietary or confidential packages.
Vulnerability data provided by Mend.io and OSV.dev.
Plugin source code © 2024, JetBrains s.r.o..
Description from the JetBrains Marketplace listing.
- Code Editing
- Maven
- Security
README badge
Show your rank in a README or on your website. The badge updates automatically.
Charts
Images: 30d · 1y · all time · 1600×900 dark
Adoption over time
7/30/90-day growth
Ranking history
Ratings over time
Listing placement
Listing placement
Listing placement
Listing placement
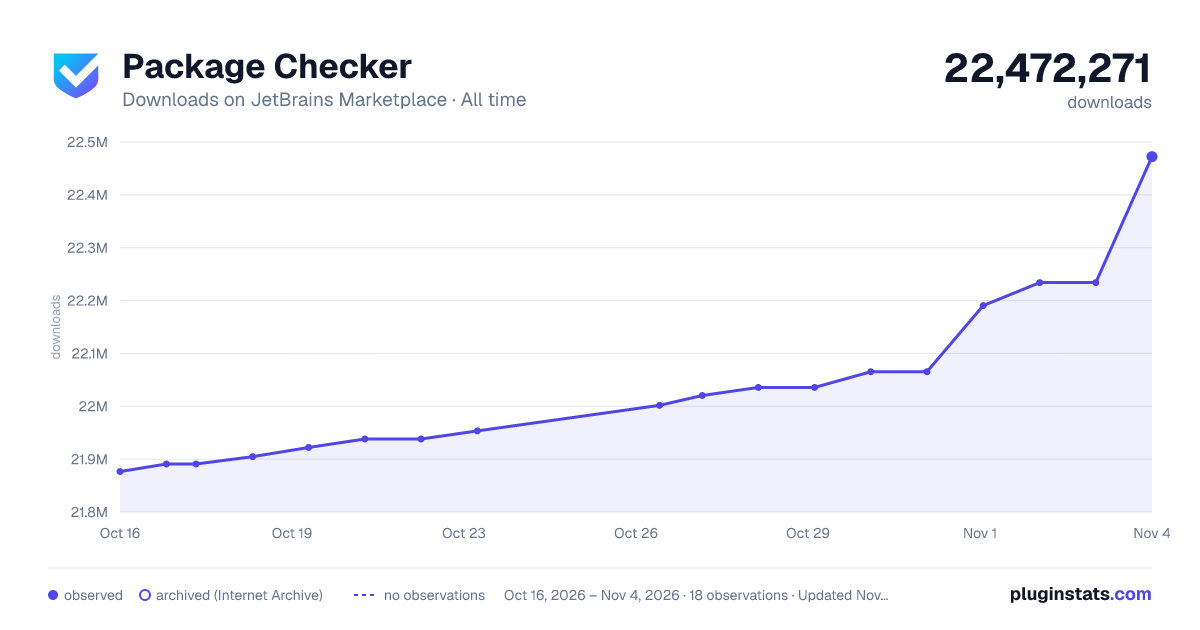
Filled points are observed values; hollow points come from Internet Archive snapshots of the listing page. Dashed segments span periods with no observations — values between points are not interpolated.
Each band is one page of 20. Downloads on a linear scale. Placement is projected from downloads, so it can differ from the marketplace's own sort order. Hover a dot to see the listing.
Recent observations
Full history (5)Similar JetBrains Marketplace Code Editing plugins
All 20 Package Checker alternatives



Data source
Cumulative download counts come from the public JetBrains Marketplace API. JetBrains reports downloads, not active installs. Ratings are the mean of public votes.
Listing: https://plugins.jetbrains.com/plugin/18337-package-checker. First seen Oct 16, 2026; last successful collection Oct 20, 2026. See the methodology.