 PluginStats
solSentinel.io installs statistics
By JoshontheWebb · GitHub Marketplace
Automatic Solidity security scanning for every pull request. Finds vulnerabilities, maps to SWC, references real exploits
solSentinel.io has 7 recorded installs on GitHub Marketplace.
It ranks #1091 of 1,393 tracked GitHub Marketplace listings by installs.
PluginStats has 1 daily observations since Oct 16, 2026; the latest is from Oct 16, 2026.
About solSentinel.io
SolSentinel automatically scans Solidity files in your pull requests for security vulnerabilities. Every PR that touches .sol files gets a detailed comment with severity ratings, SWC Registry references, and real-world exploit context — showing which DeFi hacks exploited each vulnerability type and how much was lost. Free for all repositories with zero configuration. Install on any repo or org and scans run automatically on every PR open, sync, and reopen.
Capabilities
• Automatically scans every pull request that modifies Solidity (.sol) files • Runs Wake and Solhint static analysis engines on changed files • Posts a PR comment with a severity breakdown table (Critical, High, Medium, Low) • Maps each finding to the public SWC Registry with direct links • References real-world DeFi exploits and loss amounts for each vulnerability type • Generates a permalink scan report for every PR scan • Skips test files, mocks, migrations, and libraries automatically
Benefits
• Catch vulnerabilities before merge: Every PR gets scanned before it reaches your main branch • Understand real risk: Exploit references show your team what actually happened when these bugs shipped to mainnet • Zero setup required: No config files, no CI pipeline changes, no tokens to manage — just install and go • Tier-aware depth: Free tier runs Wake + Solhint. Link your SolSentinel account at solsentinel.io to unlock Mythril, Foundry fuzz testing, and higher scan limits
Getting Started
Requirements:
• Plan: Free — no paid plan required • User Permissions: Repository read access and pull request write access (for posting comments) • Availability: Generally available
Setup Process:
• Install SolSentinel on your repository or organization • Open a pull request that adds or modifies any .sol file • SolSentinel automatically posts a security scan comment on the PR within seconds
Example Usage
SolSentinel runs automatically — no prompts needed. Here is what happens when you open a PR:
• PR with a reentrancy bug → comment shows "Critical: Reentrancy vulnerability" with SWC-107 link and reference to The DAO hack ($60M lost) • PR with an unchecked return value → comment shows "Medium: Unchecked call return" with SWC-104 link • Clean PR with no issues → comment shows "No issues detected across 3 Solidity file(s)"
Description from the GitHub Marketplace listing.
- Security
- Code Scanning Ready
Where solSentinel.io sits in the listing
Each band is one page of 20. Installs on a log scale. Placement is projected from installs, so it can differ from the marketplace's own sort order. Hover a dot to see the listing.


Charts
Images: 30d · 1y · all time · 1600×900 dark


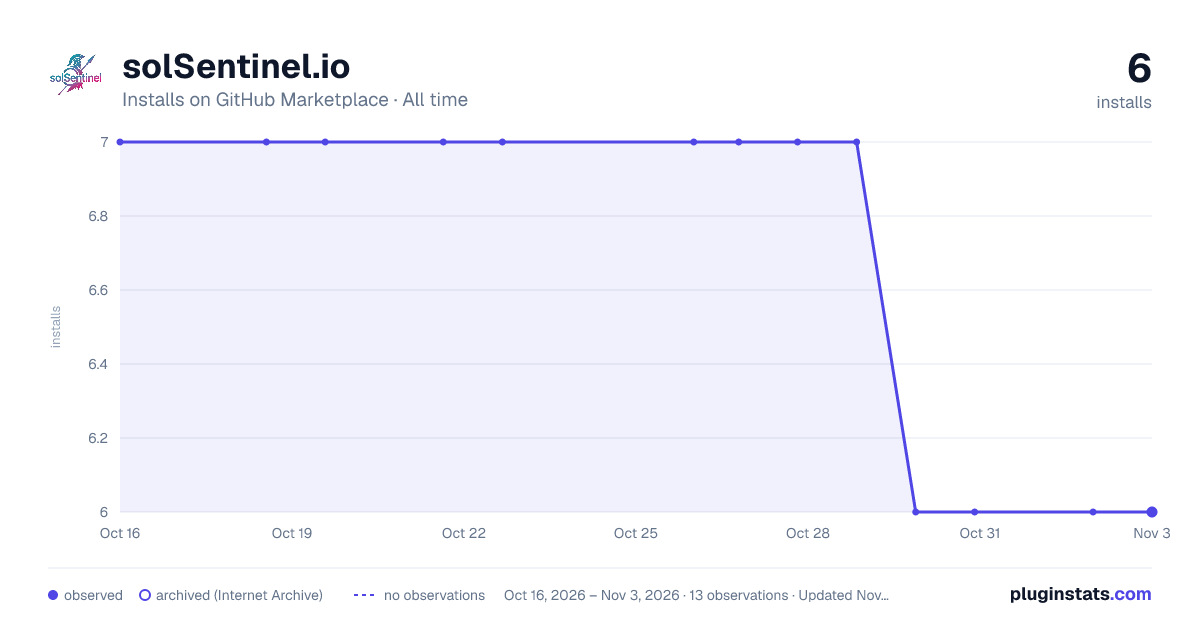

Adoption over time


7/30/90-day growth


Filled points are observed values; hollow points come from Internet Archive snapshots of the listing page. Dashed segments span periods with no observations — values between points are not interpolated.
Recent observations
Full history (1)Similar GitHub Marketplace plugins
Data source
Install counts (installations of each GitHub App across accounts and organizations) are read from public GitHub Marketplace listing pages. GitHub does not publish ratings. Category positions reflect GitHub's own popularity sort.
Listing: https://github.com/marketplace/solsentinel-io. First seen Oct 16, 2026; last successful collection Oct 16, 2026. See the methodology.