 PluginStats
Bright Security Agent installs statistics
By Bright Security (2 listings) · GitHub Marketplace
Bright agent for dynamic security scanning, fixing confirmed issues, and validating remediations
Bright Security Agent has 108 recorded installs on GitHub Marketplace, ranking #483 of 1,410 tracked listings.
About Bright Security Agent
Bright Security Agent is an autonomous agent for dynamic application and API security testing directly in your GitHub environment. It analyzes your repository, builds and starts the application from source, automatically configures authentication, registers entrypoints, runs scans via Bright Repeater, and, if needed, proposes fixes for discovered vulnerabilities.
Key Features
• Automated dynamic application security testing: Tests web apps, APIs, MCP tools, GRPC, GraphQL, etc... • AI-Powered Speed: Fast, intelligent scanning powered by deterministic scanner. • Remediation & Validation: In full mode, the agent not only finds vulnerabilities but also proposes fixes and validates them for up to 5 rounds. • Flexible Modes: • full: Complete cycle—startup, scan, remediation, validation (with harness fallback). • dynamic: Full startup and scan without fallback. • function: Scan individual functions via harness. • Security by Design: All actions are performed only against local targets (localhost, 127.0.0.1, etc.), never external/production addresses. • OIDC: Secure authentication via GitHub, no secrets stored in the repository.
Why Choose Bright
• Actionable Security Insights: Get clear, prioritized findings with remediation guidance, not noise. • Comprehensive Coverage: Detects both common and advanced vulnerabilities, including business logic flaws. • Seamless Developer Experience: Easy to use, integrates with your workflow, and requires minimal setup. • Secure by Default: Designed to run only against local, non-production targets, keeping your environment safe.
How It Works
• Detects and starts the target application from source. • Performs required setup and configuration steps. • Configures and verifies authentication. • Registers entrypoints and forms a scan plan. • Runs dynamic security testing via Bright Repeater. • Collects and analyzes results, proposes fixes, and re-validates them.
Usage Examples
• Full scan and remediation
"Run a dynamic security scan for this application, fix the findings, and validate the fixes."
• Pull request validation
"@bright-security-agent, scan the controllers affected by this pull request and fix any vulnerabilities found."
Description from the GitHub Marketplace listing.
- Security
- Agent apps
README badge
Show your rank in a README or on your website. The badge updates automatically.
Charts
Images: 30d · 1y · all time · 1600×900 dark


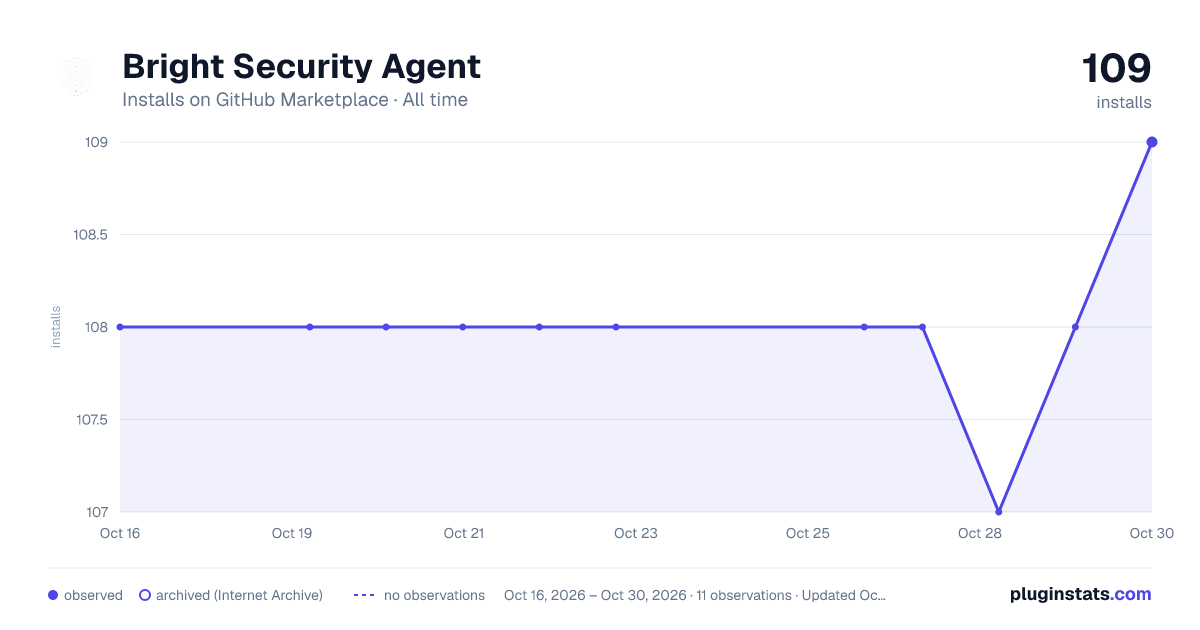

Adoption over time
7/30/90-day growth
Ranking history
Listing placement
Filled points are observed values; hollow points come from Internet Archive snapshots of the listing page. Dashed segments span periods with no observations — values between points are not interpolated.
Each band is one page of 20. Installs on a linear scale. Placement is projected from installs, so it can differ from the marketplace's own sort order. Hover a dot to see the listing.
Recent observations
Full history (2)Similar GitHub Marketplace plugins
All 20 Bright Security Agent alternativesData source
Install counts (installations of each GitHub App across accounts and organizations) are read from public GitHub Marketplace listing pages. GitHub does not publish ratings. Category positions reflect GitHub's own popularity sort.
Listing: https://github.com/marketplace/bright-security-agent. First seen Oct 16, 2026; last successful collection Oct 19, 2026. See the methodology.